Hello everyone!
We are excited to announce a series of updates related to user management that aim to make ActivityInfo more flexible, transparent and efficient, especially for organizations with complex governance structures.
Here is a quick summary of the latest ActivityInfo user management updates:
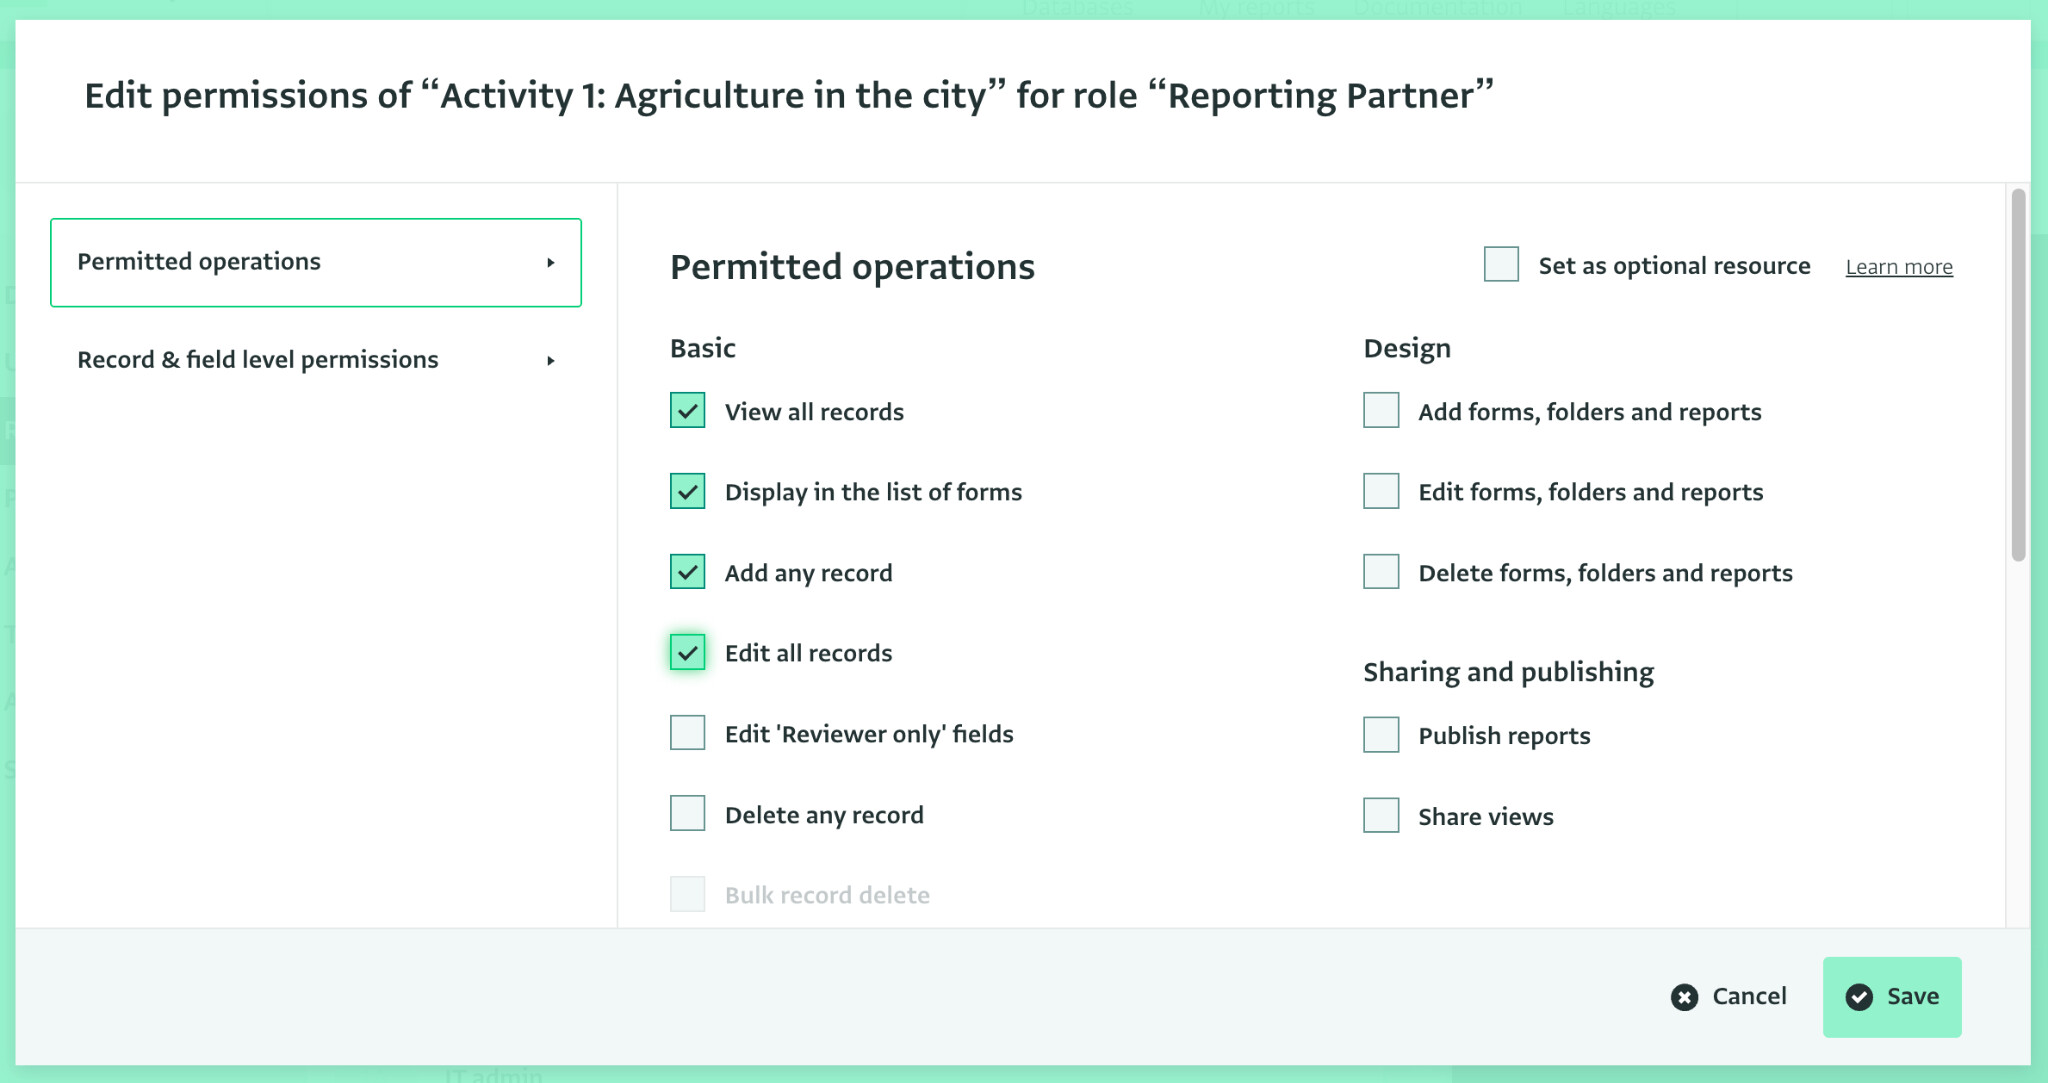
- Updated Role Design Interface: The card editor has been replaced with a modal interface, giving you a cleaner view and more space to design roles and set permissions.
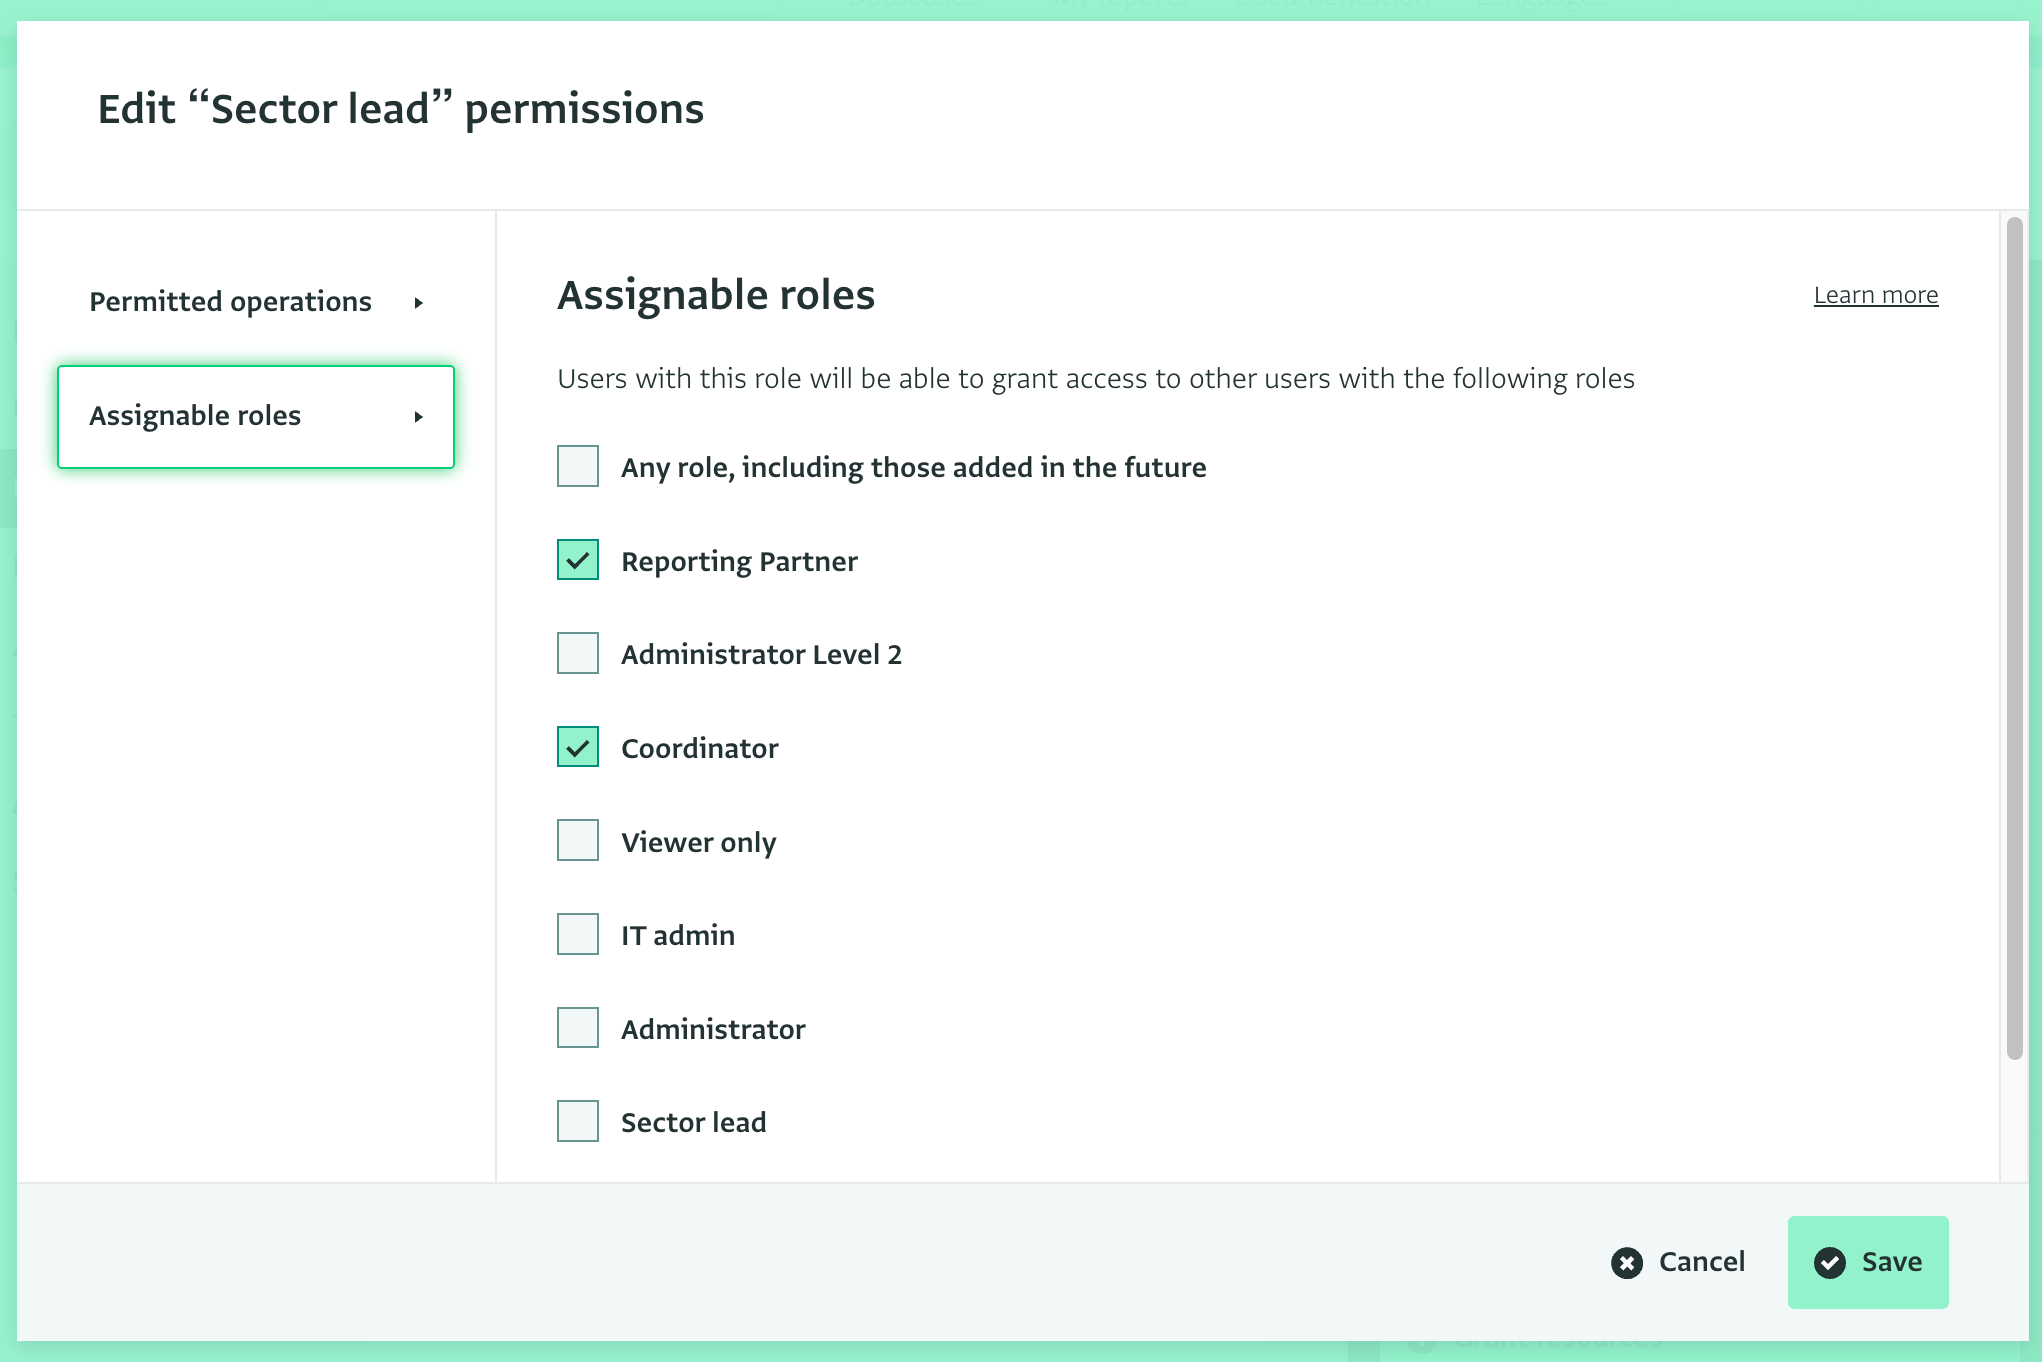
- Explicit ‘Manage Users’ Control: You can now configure exact Assignable Roles for user managers, giving you precise control over which roles specific admins (like IT or department leads) can grant.
-
Data-Preserving Access Revocation: The “Delete user” action has been renamed to “Revoke access.” Revoking access frees up your license seat and blocks access, but preserves the user’s name in ‘User’ fields and record edit histories. This can also be reverted via the audit log.
-
Changes to Database Ownership: Newly created databases will no longer have an unrestricted “database owner.” Instead, the user who created the database will be assigned to a role within the database. While existing databases retain their owners for now, database owners are strongly recommended to revoke ownership by adding themselves as a role-based user, as individual ownership is being phased out for improved data control.
-
Dedicated ‘Security Contact’ Permission: You can now assign a specific permission to team members who need security alerts (such as risk reports, transfer notifications, and dark web monitoring alerts). Existing database owners will also continue to receive these.
If you have any questions, let us know below! And if you require technical support on your specific database, you can always reach out to our Helpdesk via your Helpdesk Contact.